Screenshots show the Serbian version of the app.
Map data and its purpose
List the data used by reception, trainers, managers and the owner. For each field, document its purpose, legal basis, who sees it and how long it is retained.
If your team cannot explain why it needs data, do not collect it out of habit. The EDPB minimisation principle calls for data that is adequate, relevant and limited to its purpose.
| Data | Typical purpose | Control |
|---|---|---|
| Contact | member account and agreed communication | accuracy and consent by channel |
| Membership and payment | service delivery and records | roles and retention period |
| Visit | entry, security and operational reporting | restricted access and aggregation |
| Napomena | a specific operational need | no unnecessary sensitive details |
Roles and least privilege
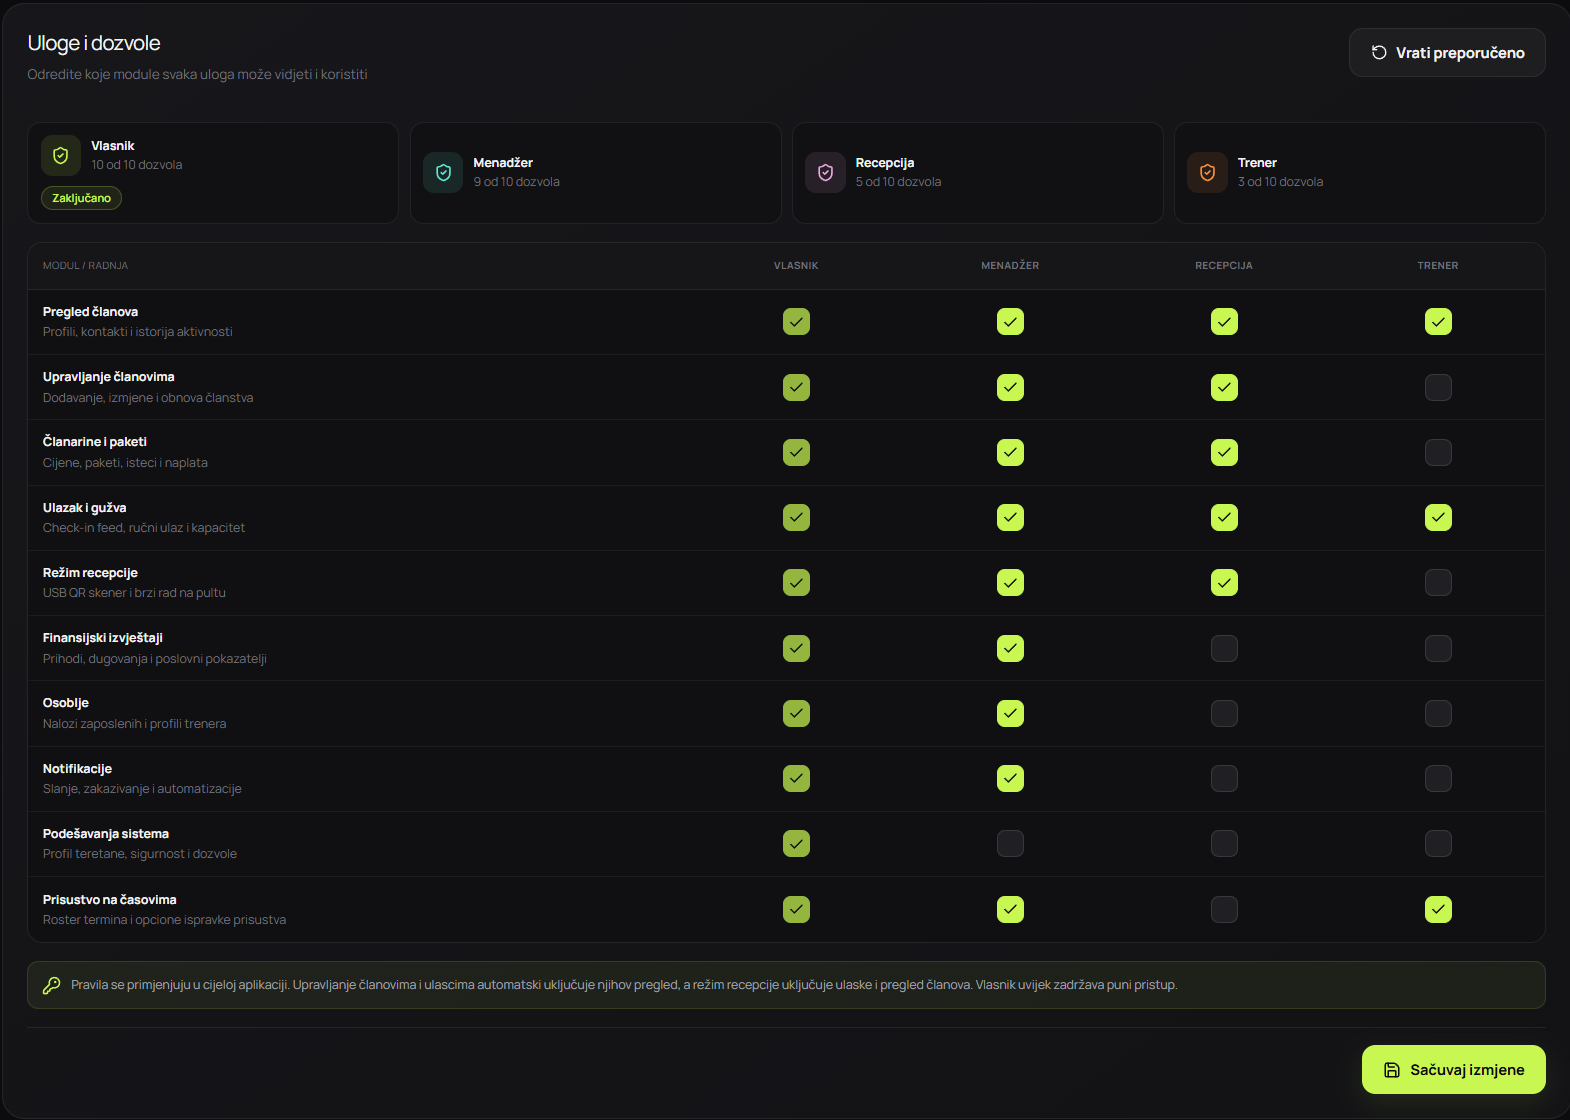
Reception staff, trainers, managers and owners do not need identical access. Each employee should use their own account so it can be revoked independently and audit records remain meaningful.
Review permissions periodically and immediately after role changes or departure. OWASP recommends checking authorisation on every request and denying access by default unless explicitly permitted.
- an individual account for each person
- minimum necessary access
- multi-factor authentication where available
- immediate removal of outdated permissions
- regular review of administrator roles
Auditing, retention and backups
Record security and business events such as sign-ins, failed authorisation, role changes, membership edits, exports and deletion. Logs should not copy passwords, full message contents or unnecessary data.
When data is no longer needed, delete or irreversibly anonymise it. Pseudonymised data can still be personal data if the person can be identified again. Deletion from the active system and backup expiry are different events.
Test procedures before an incident
At least annually or after major changes, test member data export, correction, deletion, staff account revocation and backup recovery. Record the result and next corrective action.
Define where staff report suspicious access, lost devices or incorrectly sent exports. Prompt internal reporting is more useful than a procedure nobody can find.
- access or correction requests
- deletion and legal exceptions
- incidents and internal escalation
- recovery and integrity checks
- notifying authorities and affected people where applicable